Phoenix Security is now Phoenix Security a transformative Contextual Vulnerability management platform from code to cloud
Phoenix Security’s context-based vulnerability management platform helps clients focus on the 10% of vulnerabilities that matters, from code to cloud.
LONDON, LONDON, ENGLAND, EINPresswire.com/ — LONDON, England (January 10, 2023) – Phoenix Security is excited to announce that it has rebranded from Phoenix Security, reflecting the evolution of its smart software security platform.
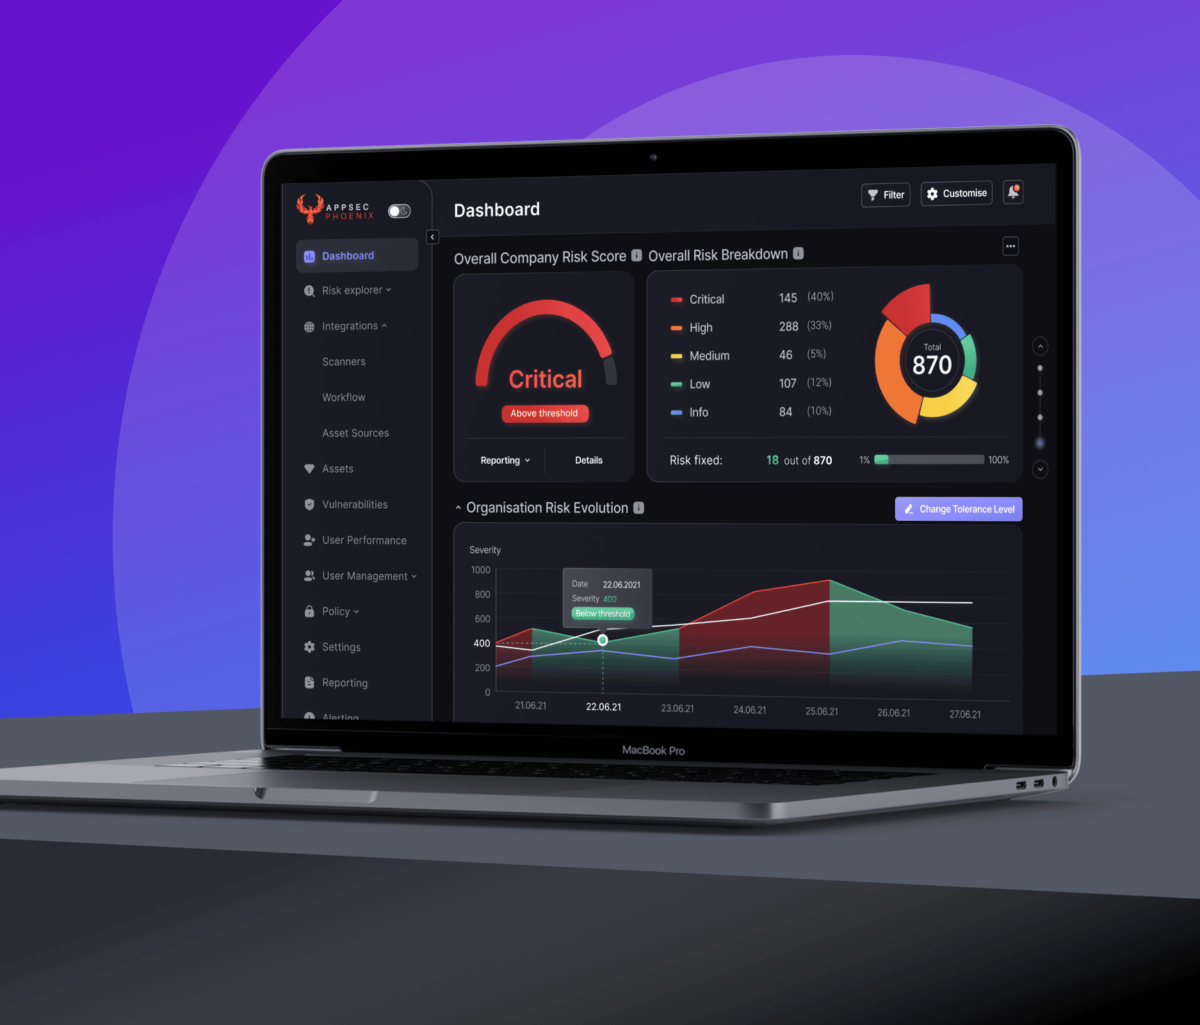
Initially launched in September 2022 as a solution for appsec and cloudsec, Phoenix Security has since evolved into a complete endpoint management platform that identifies vulnerabilities from code to cloud and prioritizes them for resolution. The platform also provides traceability for user fixing, helping clients optimize their use of security professionals and streamline their vulnerability management process.
Phoenix Security is on a mission to prevent burnout, contextualize vulnerabilities, and help security professionals and developers act on the risks and vulnerabilities that matter most. The company was established to provide an effective all-in-one security solution for application developers and businesses, and its platform connects to repositories, scanners, and the cloud to provide a prioritized list of vulnerabilities that need to be addressed first. The rebranding to Phoenix Security reflects the expanded capabilities of the platform and aligns with the company’s philosophy of cyber risk quantification, risk-driven action, and vulnerability prioritization.
I’ve chosen phoenix as a name and a symbol of reborn, the choice was right as we evolve from application security, and cloud contextualization in full stack vulnerability prioritizing platform”
Francesco Cipollone
The decision to rebrand was made as the company approaches the end of its second year and prepares for the launch of V3, which introduces new features that enhance team visibility and streamline vulnerability management even further. “We initially chose the phoenix as a symbol of renewal and rebirth, and as our platform has evolved, we felt it was appropriate to evolve the name as well,”
Said Francesco Cipollone, the founder of Phoenix Security. “We believe in the power of community, so we asked our supporters to help us choose a new name that reflects the capabilities of our platform. The overwhelming response was in favour of Phoenix Security, and we are thrilled to adopt this new identity.” Discover how Phoenix Security helps CISOs and developers remove friction and maximize the use of DevSecOps professionals at Phoenix Security
Get in control of your Application Security posture and Vulnerability management
Phoenix Security risk based vulnerability management for application and cloud security
Phoenix Security was established to provide an effective all-in-one security solution for application developers and businesses. Phoenix helps start-ups and enterprises solve complex software security supply chain visibility by averaging the power of Correlation and contextualisation. Phoenix Platform connects to your repositories, scanners, and cloud correlates all the information and provides you with a prioritised list of vulnerability that needs to be addressed first. Discover how Phoenix Security helps CISOs and developers remove friction and maximise the use of DevSecOps professionals at https://phoenix.security Phoenix Security, Correlate, contextualise and act on risk with one click.
Francesco is an internationally renowned public speaker, with multiple interviews in high-profile publications (eg. Forbes), and an author of numerous books and articles, who utilises his platform to evangelize the importance of Cloud security and cutting-edge technologies on a global scale.
Francesco is an internationally renowned public speaker, with multiple interviews in high-profile publications (eg. Forbes), and an author of numerous books and articles, who utilises his platform to evangelize the importance of Cloud security and cutting-edge technologies on a global scale.
CVE-2026-119618 (HTTP2Reset) lets one unauthenticated HTTP/2 request corrupt the heap of Apache HTTP Server 2.4.55 to 2.4.70. Public labs crash workers on demand, and attacker bytes reach a dereferenced pointer. The fix in 2.4.71 is one line, but only servers that actually speak HTTP/2 are reachable.
Node.js fixed 16 runtime vulnerabilities on November 11, 2026, and 7 are High. CVE-2026-123864 can leak TLS private keys and other users’ requests from HTTPS servers. CVE-2026-123863 crashes a default HTTP/2 server with one unauthenticated request. There is no workaround: upgrade to 22.23.5, 24.22.3 or 26.13.1.
The wfx campaign used 4,837 hijacked GitHub accounts to plant a CI credential stealer in 8,093 repositories. It ran in at least 1,806, took secrets and cloud keys, then deleted itself within minutes. There is no CVE, and AWS and Azure backdoors survive secret rotation.
Frontier models made vulnerability discovery cheap: 948 Linux privilege escalations at about $1,280 each. Fixing didn’t speed up. Only 1 in 8 disclosed AI findings has a known upstream patch, and AI-found bugs are exploited at 1.3%, the historical norm. The bottleneck is verified remediation, owned by a team and proven by the next scan.
CVE-2026-98432 is a pre-authentication use-after-free in the Linux kernel’s IPv4 TCP handshake, present since kernel 4.4 and shown to reach remote root on MPTCP listeners. In 15 days Red Hat moved its score from 5.9 to 9.8 with no code change. Here is why the scores split and how to patch.
Freezers forced to 50°C, a fake coding test that reached a wallet signer, a tampered IDE extension. No shared attacker, one pattern: ordinary access, extraordinary authority. Here is what the CRA asks of you in 24 hours, and how we run it in Phoenix Orange.
Derek Fisher – Head of product security at a global fintech. Speaker, instructor, and author in application security.
Derek is an award winning author of a children’s book series in cybersecurity as well as the author of “The Application Security Handbook.” He is a university instructor at Temple University where he teaches software development security to undergraduate and graduate students. He is a speaker on topics in the cybersecurity space and has led teams, large and small, at organizations in the healthcare and financial industries. He has built and matured information security teams as well as implemented organizational information security strategies to reduce the organizations risk.
Derek got his start in the hardware engineering space where he learned about designing circuits and building assemblies for commercial and military applications. He later pursued a computer science degree in order to advance a career in software development. This is where Derek was introduced to cybersecurity and soon caught the bug. He found a mentor to help him grow in cybersecurity and then pursued a graduate degree in the subject.
Since then Derek has worked in the product security space as an architect and leader. He has led teams to deliver more secure software in organizations from multiple industries. His focus has been to raise the security awareness of the engineering organization while maintaining a practice of secure code development, delivery, and operations.
In his role, Jeevan handles a range of tasks, from architecting security solutions to collaborating with Engineering Leadership to address security vulnerabilities at scale and embed security into the fabric of the organization.
Jeevan Singh is the Director of Security Engineering at Rippling, with a background spanning various Engineering and Security leadership roles over the course of his career. He’s dedicated to the integration of security practices into software development, working to create a security-aware culture within organizations and imparting security best practices to the team. In his role, Jeevan handles a range of tasks, from architecting security solutions to collaborating with Engineering Leadership to address security vulnerabilities at scale and embed security into the fabric of the organization.
James Berthoty has over ten years of experience across product and security domains. He founded Latio Tech to help companies find the right security tools for their needs without vendor bias.
Chris Romeo is a leading voice and thinker in application security, threat modeling, and security champions and the CEO of Devici and General Partner at Kerr Ventures. Chris hosts the award-winning “Application Security Podcast,” “The Security Table,” and “The Threat Modeling Podcast” and is a highly rated industry speaker and trainer, featured at the RSA Conference, the AppSec Village @ DefCon, OWASP Global AppSec, ISC2 Security Congress, InfoSec World and All Day DevOps. Chris founded Security Journey, a security education company, leading to an exit in 2022. Chris was the Chief Security Advocate at Cisco, spreading security knowledge through education and champion programs. Chris has twenty-six years of security experience, holding positions across the gamut, including application security, security engineering, incident response, and various Executive roles. Chris holds the CISSP and CSSLP certifications.
Jim Manico is the founder of Manicode Security, where he trains software developers on secure coding and security engineering. Jim is also the founder of Brakeman Security, Inc. and an investor/advisor for Signal Sciences. He is the author of Iron-Clad Java: Building Secure Web Applications (McGraw-Hill), a frequent speaker on secure software practices, and a member of the JavaOne Rockstar speaker community. Jim is also a volunteer for and former board member of the OWASP foundation.
Join our Mailing list!
Get all the latest news, exclusive deals, and feature updates.