Join our Mailing list!
Get all the latest news, exclusive deals, and feature updates.
AI-Native SDLC Security
We're at LASCON in Austin. Come by and see how hooks catch criticals while the code is still being written. Then stay for Francesco's talk, our after party, a book signing and the raffle.

40 to 800: securing the AI-native SDLC. Red Oak Ballroom.
Learn moresouthBeer and snacks on us at Celis Brewery, right after the talk.
Registernorth_eastGet the AI-Native SDLC Security Program signed by Francesco and Cameron.
Learn moresouthA LEGO Ghostbusters set, two LED backpacks and an Amazon gift card.
Learn moresouthWhat's a hook
A hook is a small check that runs at one exact moment, like right before an agent saves a file. Our team went from 40 to 800 commits per developer a month, so the checks moved to where the code is written. Hooks are cheap, they run first, and they cut the token bill.
SAST, SCA and autofix for AI-written code. Flaws get caught and fixed while the agent is still on the task.
Know morearrow_forwardOne risk picture across SAST, SCA, containers and cloud. Scored by what attackers actually exploit.
Know morearrow_forwardA supply chain firewall for developer machines. Malicious packages get stopped before they reach the laptop.
Know morearrow_forwardEvery finding gets an owner and a business impact. Fix what matters first, and prove the burn-down.
Know morearrow_forwardFixes arrive as pull requests your team reviews and merges. People stay in charge of what ships.
We'll show you where hooks catch criticals in your setup, on a real account.
Book a demoarrow_forwardFrancesco's talk
Fifty minutes on what changed when our build speed went up twenty times. Vendor-neutral. Human first, AI second.
Free ice cream at Francesco's talk, while it lasts.
We went from 40 commits per developer a month to 800, with the same headcount. Code went from 40,000 lines to 400,000. Going faster was the easy part. Staying secure at that speed was the real work.
Build got fast. Plan, design, review and deploy did not. So we used the time we got back to move security off the end of the pipeline and into every one of seven stages. The end-of-cycle scan is still there. It just stopped being the safety net and became the check that proves the work was already secure.
What Francesco will cover
What you'll take home
Phoenix After Party
You got caught by Francesco's talk. We're not letting you go. Beer and snacks are on us.

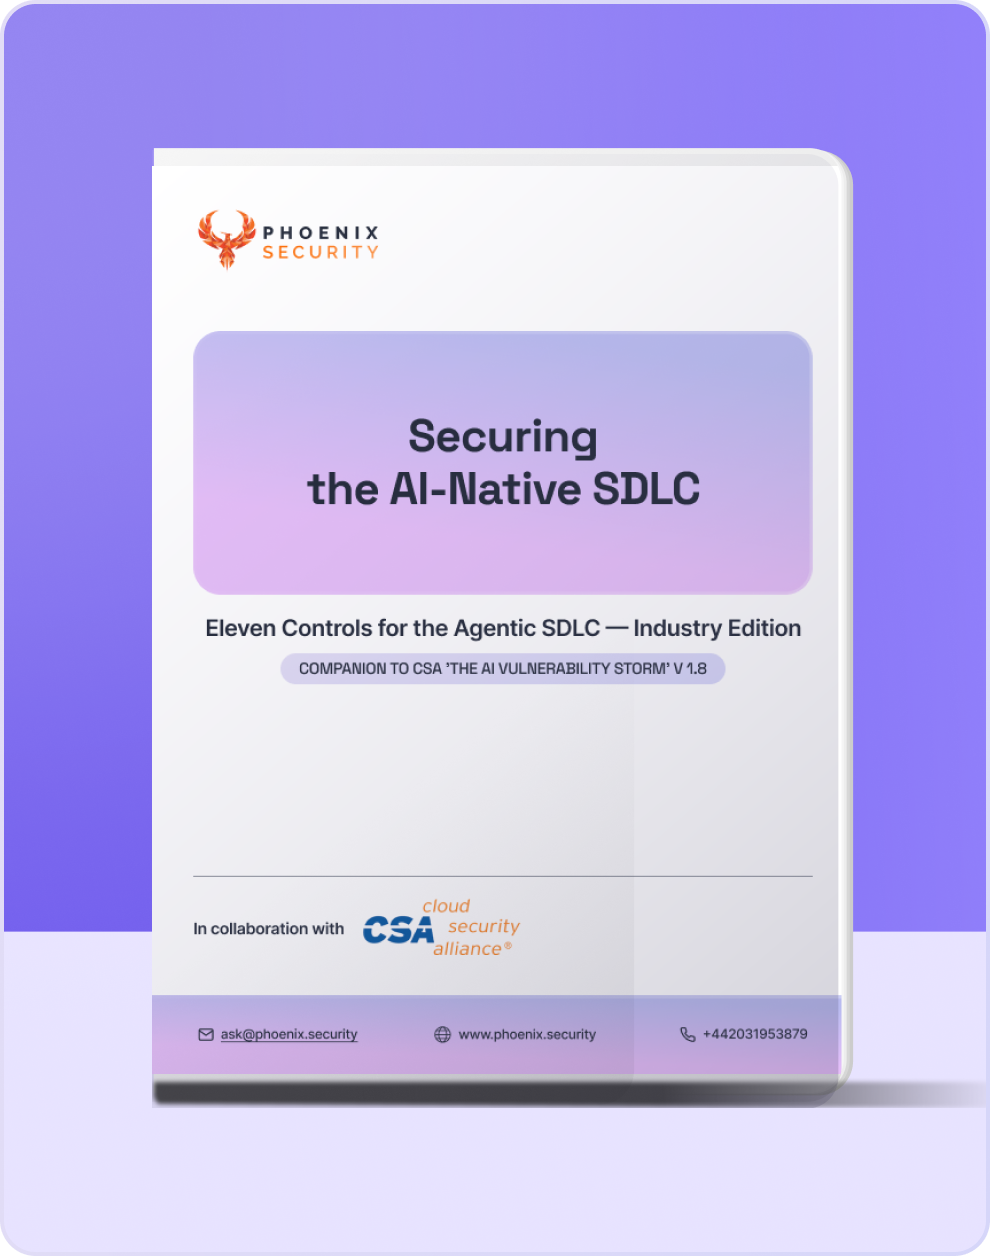
Get your copy signed
We built this program with the Cloud Security Alliance. It goes with CSA's paper "The AI Vulnerability Storm".
Coding agents now write a big part of production code. The program does two jobs. It stops new vulnerabilities from getting in, and it burns down the backlog you already have.
Phoenix raffle
Paper tickets, a locked box and a live draw at our table. It takes about a minute to enter.

The big one. Clear a shelf.

One each for two lucky people

Spend it on whatever you want
Write your name, email and company on the ticket.
Keep your number. You'll need it at the draw.
The draw is Friday, Oct 30 at 2:00 PM, right at our table.
This is Steve. Still waiting for TeamPCP to take a day off.
Come for the book signing at 1:30 and you're already in the right spot.
Booth giveaway
Come by table #11 and grab something for the road. Pocket fans for a warm expo hall, a sticker set for your laptop, and our new t-shirt. All free, while they last. The fans always go first.
Pocket fans


See you in Austin
Grab a fan, drop a ticket in the box and tell us about your pipeline. Then grab a beer with us after Francesco's talk.

Derek Fisher – Head of product security at a global fintech. Speaker, instructor, and author in application security.
Derek is an award winning author of a children’s book series in cybersecurity as well as the author of “The Application Security Handbook.” He is a university instructor at Temple University where he teaches software development security to undergraduate and graduate students. He is a speaker on topics in the cybersecurity space and has led teams, large and small, at organizations in the healthcare and financial industries. He has built and matured information security teams as well as implemented organizational information security strategies to reduce the organizations risk.
Derek got his start in the hardware engineering space where he learned about designing circuits and building assemblies for commercial and military applications. He later pursued a computer science degree in order to advance a career in software development. This is where Derek was introduced to cybersecurity and soon caught the bug. He found a mentor to help him grow in cybersecurity and then pursued a graduate degree in the subject.
Since then Derek has worked in the product security space as an architect and leader. He has led teams to deliver more secure software in organizations from multiple industries. His focus has been to raise the security awareness of the engineering organization while maintaining a practice of secure code development, delivery, and operations.
In his role, Jeevan handles a range of tasks, from architecting security solutions to collaborating with Engineering Leadership to address security vulnerabilities at scale and embed security into the fabric of the organization.

Jeevan Singh is the Director of Security Engineering at Rippling, with a background spanning various Engineering and Security leadership roles over the course of his career. He’s dedicated to the integration of security practices into software development, working to create a security-aware culture within organizations and imparting security best practices to the team.
In his role, Jeevan handles a range of tasks, from architecting security solutions to collaborating with Engineering Leadership to address security vulnerabilities at scale and embed security into the fabric of the organization.

James Berthoty has over ten years of experience across product and security domains. He founded Latio Tech to help companies find the right security tools for their needs without vendor bias.


Chris Romeo is a leading voice and thinker in application security, threat modeling, and security champions and the CEO of Devici and General Partner at Kerr Ventures. Chris hosts the award-winning “Application Security Podcast,” “The Security Table,” and “The Threat Modeling Podcast” and is a highly rated industry speaker and trainer, featured at the RSA Conference, the AppSec Village @ DefCon, OWASP Global AppSec, ISC2 Security Congress, InfoSec World and All Day DevOps. Chris founded Security Journey, a security education company, leading to an exit in 2022. Chris was the Chief Security Advocate at Cisco, spreading security knowledge through education and champion programs. Chris has twenty-six years of security experience, holding positions across the gamut, including application security, security engineering, incident response, and various Executive roles. Chris holds the CISSP and CSSLP certifications.

Jim Manico is the founder of Manicode Security, where he trains software developers on secure coding and security engineering. Jim is also the founder of Brakeman Security, Inc. and an investor/advisor for Signal Sciences. He is the author of Iron-Clad Java: Building Secure Web Applications (McGraw-Hill), a frequent speaker on secure software practices, and a member of the JavaOne Rockstar speaker community. Jim is also a volunteer for and former board member of the OWASP foundation.
Get all the latest news, exclusive deals, and feature updates.